ISO/IEC 27001 Certification
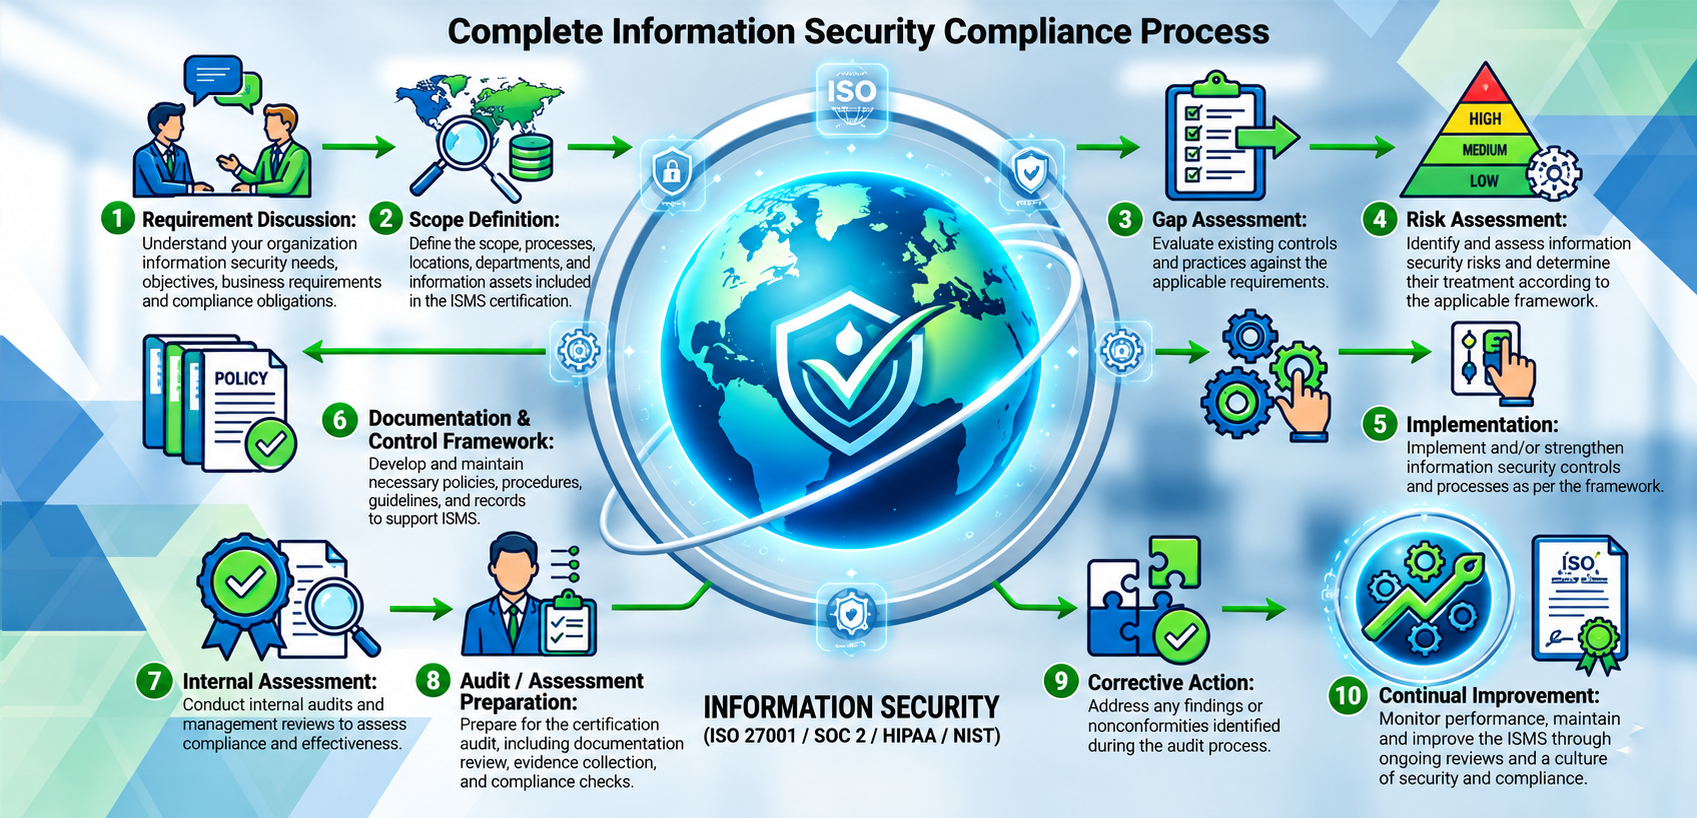
ISO/IEC 27001 is an internationally recognized standard for Information Security Management Systems (ISMS).
It provides a systematic framework for organizations to identify information security risks, implement appropriate controls, monitor security performance and continually improve their information security management system.
ISO 27001 can be relevant to:
IT CompaniesSoftware CompaniesSaaS BusinessesCloud Service ProvidersBPO & KPOFinancial ServicesHealthcare OrganizationsData-Driven BusinessesTechnology CompaniesOrganizations Handling Sensitive Customer or Business Information
02
VAPT – Vulnerability Assessment & Penetration Testing
Vulnerability Assessment and Penetration Testing (VAPT) helps organizations identify security vulnerabilities in applications, networks, systems and other technology environments.
VAPT can help organizations understand potential weaknesses and prioritize remediation actions.
Depending on the scope, VAPT may cover:
Web ApplicationsMobile ApplicationsNetwork InfrastructureServersAPIsCloud EnvironmentsIT Infrastructure
Organizations may use VAPT as part of their cybersecurity, customer security assessment or compliance programs.
03
STQC Certification & Consultancy
STQC (Standardisation Testing and Quality Certification) provides testing, quality assurance and certification-related services in the area of electronics and IT.
Organizations may need to address applicable STQC requirements depending on their products, systems, projects or government-related requirements.
SHRINIVAS ENTERPRISES provides consultancy assistance to help organizations understand applicable requirements and prepare relevant documentation and processes.
04
GDPR Compliance Consultancy
The General Data Protection Regulation (GDPR) establishes requirements concerning the processing and protection of personal data within its scope.
Organizations handling personal data of individuals in relevant jurisdictions may need to assess their obligations and implement appropriate privacy and security measures.
Our GDPR consultancy can support organizations with understanding applicable requirements, privacy processes, data protection controls and compliance preparation.
05
SOC 1 & SOC 2 Compliance
SOC 1 and SOC 2 are assurance frameworks used to provide information about controls within service organizations.
SOC 1 is generally focused on controls relevant to financial reporting, while SOC 2 addresses controls related to areas such as security and other applicable trust services criteria.
They can be particularly relevant to:
SaaS CompaniesCloud Service ProvidersIT Service ProvidersData Processing CompaniesBPO OrganizationsTechnology Service ProvidersOrganizations Serving Enterprise Customers
SHRINIVAS ENTERPRISES can provide consultancy guidance to help organizations understand applicable control requirements and prepare their processes for an appropriate assessment.